The Binance hacker holds more ETH than it took
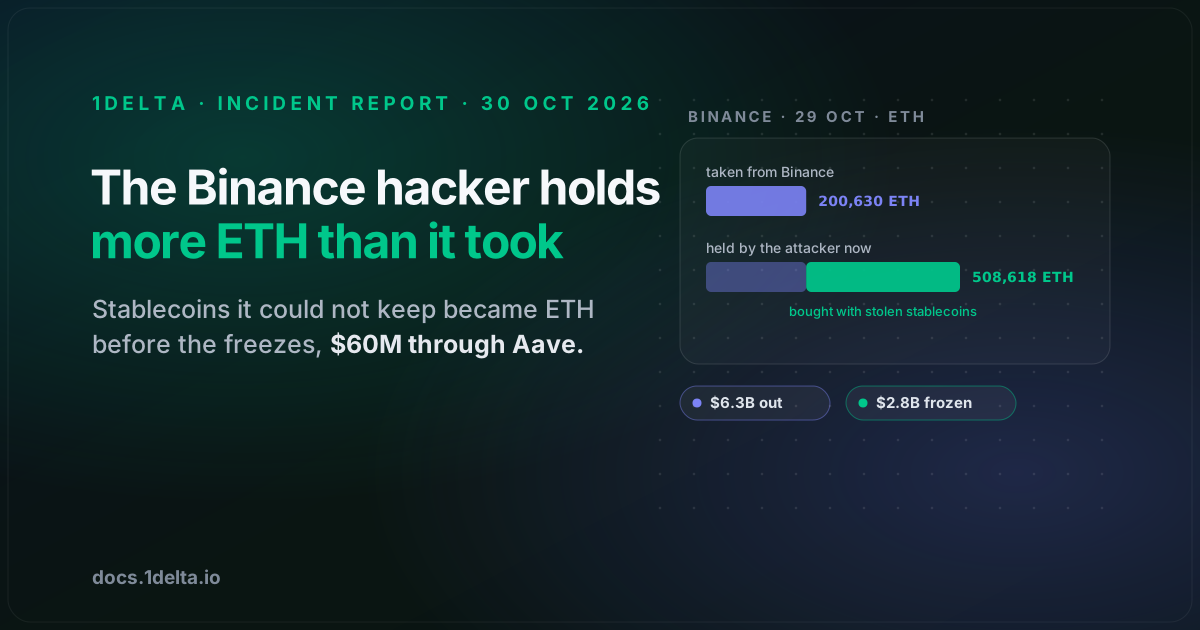
On 29 October about $6.3B left Binance's hot wallets on ten chains. The attacker took 200,630 ETH and now holds 508,618: the stablecoins it could not keep were turned into ETH before the freezes reached them, $60M of it through an Aave loan.
On 29 October, between 20:04 and 23:56 UTC, about $6.3B left Binance's hot wallets on ten chains. It is the largest theft on record, roughly four times the $1.5B taken from Bybit in February 2025.
The attacker took 200,630 ETH. Its wallets now hold 508,618 ETH. The difference is stolen USDT, USDC and some 150 other tokens, converted to ETH in the hour before the issuers' freezes reached them, $60M of it through a loan on Aave.
Binance has not published a root cause. This piece combines its statements with the tracing published by TRM Labs, Elliptic, Chainalysis, Bitquery and drk.vc. The Ethereum transactions, freeze times, frozen balances and the Aave position we read ourselves. Figures are as of 30 October 2026, 19:10 UTC.
What left
Estimates run from Binance's own $6.3B to Elliptic's $6.43B. TRM puts it at $6.36B, valuing each transfer at the price when it went out. About $2.8B is frozen, almost all of it stablecoins.
| chain | taken | frozen or seized |
|---|---|---|
| Ethereum | 200,630 ETH and 185 tokens, incl. 1.875B USDT and 823M USDC · $3.79B | 1,380.5M USDT, 823M USDC, 40.5M RLUSD, 27.8M USD1 |
| Bitcoin | 18,270 BTC · $1.47B | none |
| Tron | 612.7M USDT and 46.4M TRX · $628M | 378.7M USDT |
| XRP Ledger | 233.46M XRP · $296M | none |
| Solana | 970,500 SOL · $96M | none |
| Arbitrum, Optimism, Base | $39M | 8,426 ETH and 74.6M ARB, moved out by the Arbitrum Security Council |
| Avalanche | $28M | 8.4M USDt |
| Polygon | $10M | 6.2M USDT0 |
Amounts taken are TRM's. The Ethereum USDT and USDC frozen are our reads of the attacker's addresses; the other frozen figures are TRM's and Elliptic's.
The bitcoin, XRP and SOL have not moved. Bitquery found the 18,270 BTC split across 19 addresses, 17 of them holding exactly 1,000 BTC, unspent since 20:48. The XRP and Solana receiving accounts have never sent a transaction. No issuer can freeze any of it.
Binance says it has set aside more than $6.34B of company funds to cover the loss and that user funds are safe. Its SAFU fund holds 15,000 BTC, less than the 18,270 BTC the attacker now holds. Across exchanges, $1.51B of positions were liquidated in 24 hours, $1.30B of them longs (CoinGlass), and BNB fell 6.3% between 20:15 and 20:50.
How Binance 14 was emptied
Binance 14 (0x28C6…1d60) is one of Binance's busiest Ethereum hot wallets. At 20:20:59 an account the attacker had funded through Tornado Cash (0x7c86…5ca0) sent it a type-4 transaction with 50 EIP-7702 authorizations. All 50 were signed by Binance 14's key and delegated the wallet to the same contract. Each was for a different nonce, from 18,914,775 to 18,914,824. An EIP-7702 authorization is valid only at the signer's current nonce, and the wallet was sending its own transactions every few seconds, so the attacker covered a range of 50. One matched.
From that block on, Binance 14 ran the attacker's code. The contract is a sweeper: its sweep function sends the wallet's whole ETH and token balance to an address of the caller's choosing, and it accepts calls only from 0x7c86 (Blockaid, drk.vc).
The wallet kept working as a hot wallet. In the 17 blocks between the delegation and the first sweep, Binance 14 signed 15 transactions of its own and customer deposits kept arriving. At 20:24:23 the attacker called the sweeper once. The transaction emitted 63 transfers, all to one address (0x5227…2f8c), including 1,615,409,499 USDT, and moved 167,464 ETH along with them.
Binance's systems went on routing funds into Binance 14 after that, and the sweeper took them again at 21:04, 21:44 and as late as 23:56. The 21:44 sweep alone moved 200.39M USDT that Binance's own internal transfers had just sent in (drk.vc). Binance removed the delegation at 00:10:35 on 30 October by signing a new authorization that points to the zero address. Between the two, Binance 14's nonce went up by 95: for almost four hours a wallet running the attacker's code was still sending Binance's transactions.
The other chains had no delegation
Every other chain was drained by ordinary transfers carrying valid signatures from Binance's own hot wallets. Five XRP Ledger accounts went at 20:04, Solana at 20:10, Bitcoin and Tron at 20:20, Arbitrum at 20:30, and Avalanche and Polygon after 23:00. On Ethereum a second hot wallet, never delegated, signed its own transfer of 28,006 ETH to the attacker's address at 20:24:47, 24 seconds after the first sweep (drk.vc). Elliptic counts nine transfers from that wallet, worth $174M.
TRM and Elliptic both conclude that the attacker could get Binance's signing system to sign for it on several chains, rather than holding a particular key. The 50 authorizations fit that: anyone holding the key could have signed for the right nonce at the moment of sending.
Binance's account so far is that a "compromised DevOps engineer's laptop" gave the attacker access to "a service container" from which it could "submit unauthorized withdrawal transactions", and that it has found "no evidence of any wallet private key leak". A later update said the investigation had "uncovered additional points of breach", without saying where. Co-CEO Richard Teng said the attacker "did not simply use one engineer's permissions" and that the attack "was not a single 'one-click' action."
The preparation began at least 36 hours earlier. TRM and drk.vc trace three small Tornado Cash withdrawals to the operator wallet on 28 October, then test runs against attacker-controlled accounts on 29 October, the last about four hours before Binance 14 was delegated.
The race against the freezes
Stablecoins were $3.46B of the theft (Elliptic). The USDT reached the main receiver at 20:24:23 and Tether blacklisted that address at 21:01:35. Over the next 17 minutes it blacklisted seven more of the attacker's addresses, and Binance 14 itself at 22:06.
| time (UTC) | address | USDT held when frozen |
|---|---|---|
| 21:01:35 | 0x5227…2f8c (main receiver) | 971.15M |
| 21:01:35 | 0x9749…c762 | 0 |
| 21:01:47 | 0x0ddf…697e | 0 |
| 21:02:47 | 0x8d53…639a (the Aave borrower) | 0 |
| 21:12:35 | 0x7aa4…bfd1 | 0 |
| 21:14:59 | 0xaa24…54a0 | 175.0M |
| 21:16:47 | 0xccbe…a263 | 0 |
| 21:18:59 | 0xb171…c8c3 | 30.0M |
| 22:06:23 | Binance 14 | 1.35M |
Five of the eight attacker addresses were empty when the blacklist reached them. The main receiver holds 1,175.5M USDT today, 204M more than when it was frozen, because the sweeper kept pushing Binance 14's new USDT into an address that could no longer send it.
What got out before the freezes went three ways:
- Fillers and market makers. Chainalysis saw $500M of stablecoins moved to a swap wallet. Over about 20 minutes $325M of it became $285M of ETH, and the remaining $175M went to the stopover wallet Tether froze at 21:14:59. TRM traces the sale through UniswapX and other intent contracts: about 122,300 ETH, an implied $2,650 per ETH when the market was at $2,300–2,350. Elliptic counts 434M USDT sold across Uniswap, 1inch and request-for-quote desks at a 12–26% haircut.
- The rest of the sweep. Lookonchain tallied $158.25M of UNI, ENA, PEPE, LINK, AAVE, ONDO and WLD sold for 70,480 ETH. Of 88.5M RLUSD, 48M was sold on DEXs before Ripple froze the rest at 22:01.
- Tron. 234M USDT went into 638M TRX on SunSwap (Elliptic). Since 02:45 on 30 October a second wallet has been sending TRX in lots to fresh addresses that swap it back to USDT on SunSwap (Bitquery). Chainalysis describes thousands of automated transactions in which each new address first receives exactly 1 TRX.
Elliptic finds the pace unusual. In earlier North Korean thefts, stablecoins were swapped within minutes. Here the USDT sat for 37 minutes on Ethereum and 46 on Tron.
Aave: three minutes, no counterparty
The fourth way out needed no buyer. At 20:57:59 a fresh address in the attacker's cluster (0x8d53…639a) supplied 10M USDT to Aave V3's Ethereum Core market and at 20:59:11 borrowed 3,271.43 WETH. At 21:00:11 it supplied another 50M USDT, and at 21:00:59 it borrowed 16,490.99 WETH. The WETH was unwrapped and moved on. The address holds 0.00001 ETH today.
Tether blacklisted the address at 21:02:47, 108 seconds after the second borrow. By then it held no USDT. The 60M sat in Aave's aUSDT contract, which is not blacklisted, and the attacker held 60M aUSDT in its place.
By price, this exit was dearer than the fillers. The attacker got about $44.6M of ETH for 60M USDT, 74 cents on the dollar, against about 88 cents through UniswapX. It needed no quote, no counterparty and nobody's agreement. Aave's guardians froze the Ethereum Core WETH and USDT reserves at 21:47:23, 46 minutes after the borrow. In all they froze 175 V3 reserves on 16 networks and 117 V4 reserves on four, because the attacker "could swap the stolen funds into any listed asset", in Aave's words. A freeze blocks new supply and new borrowing. Repayment, withdrawal and liquidation keep working.
The position at 19:10 UTC:
| position | value |
|---|---|
| collateral | 60.01M aUSDT · $59.91M |
| debt | 19,763.44 WETH · $43.98M |
| health factor | 1.063 |
| ETH price that triggers liquidation | about $2,364 (Aave's oracle reads $2,225) |
Aave's suppliers are not exposed: the loan is over-collateralised and can be liquidated like any other. If ETH rises about 6%, liquidators repay the WETH and take the USDT plus the liquidation bonus, and the attacker keeps the ETH it borrowed. Until then about $3.5M of the collateral is more than the debt requires. A withdrawal would pay USDT out of Aave's aUSDT contract, which Tether's blacklist does not cover. None has moved, and the borrower has not touched Aave since 21:01. Binance co-founder Yi He has said the collateral is "not fully frozen" and that about $14M may be recoverable once it is released.
Aave unfroze Ethereum Core at 12:26:35 UTC on 30 October. USDT and USDC came back with a loan-to-value of zero: they can be supplied but cannot back a new loan. Aave's governance thread names nine assets kept at zero, all of them held somewhere in the attacker's cluster: USDT, USDC, USDT0, POL, WAVAX, sAVAX, XAUt, PAXG and OP. Borrow caps came back lower, following LlamaRisk's proposal to set each one 2% above pre-exploit borrowing. WETH went from 2.4M to 1.79M, USDT from 3.09B to 2.56B and USDC from 2.7B to 2.27B. Across V3 that removes about $3.7B of unused capacity, and $130M on V4, so a wallet holding half a million ETH cannot take the whole headroom in the first block after reopening.
For anyone running a lending market, three timings matter. The borrow took three minutes from an address with no history. The issuer's blacklist arrived 108 seconds later and found nothing. The protocol-wide freeze needed 46 minutes for its first reserve and until 23:04 for the guardian multisigs to finish. The freeze also caught ordinary users: between 21:49 and 22:07 holders redeemed 4.6M GHO for USDT through the GHO Stability Module, and on V4's Ethereum Core Hub Aave capped the full-utilisation borrow rate at 10% for its largest stablecoin and WETH reserves while suppliers withdrew.
Who did it
TRM ("high confidence") and Chainalysis attribute the theft to TraderTraitor, the North Korean group the FBI named for Bybit. The strongest link is an Ethereum address, 0x1510…feb7, that received funds from both this theft and Bitget's on 24 September. ZachXBT spotted it first. The Binance funds reached it from Tron through a peel chain of about 28 hops, then THORChain and the Hyperlane bridge (Elliptic).
Elliptic also attributes it to North Korea, and lists what is thin. About $39K of Binance funds reached that address, against about $510K from Bitget, which a launderer serving several clients would also explain. The slow stablecoin swaps and the use of market makers and a lending market differ from the bridge-heavy laundering after Bybit. No government has spoken, while the FBI attributed Bybit within five days. Binance has not named anyone.
What is still missing
- The root cause. What ran on the laptop, what the service container was allowed to do, and where the "additional points of breach" are.
- How one system came to sign on ten chains. Binance says no key leaked. Something produced valid signatures for XRP, Solana, Bitcoin, Tron and two Ethereum wallets within half an hour, and Binance 14 went on sending transactions for almost four hours while it ran the attacker's code.
- Withdrawals. Binance expects to reopen them about 45 hours after its 30 October update, around 1 November, and to publish an updated proof of reserves after remediation.
- The Aave collateral. Whether any of the 60M USDT returns to Binance, and on what terms.
- The unfreezable $3.3B. The ETH, BTC, XRP and SOL in the attacker's wallets have barely moved.
Bitget lost $387.5M five weeks ago through a server that was allowed to ask for signatures. Binance has described the same shape at sixteen times the size: by its account the keys held, and the system that requests signatures did not.
Sources: Binance's statements on X, its update on funds reserved and on further breach points and withdrawal timing; Richard Teng's remarks via The Hacker News; Yi He on the Aave collateral via KuCoin News. Tracing: TRM Labs, Elliptic, Chainalysis, Bitquery, drk.vc, Blockaid on X, ZachXBT on X, and Lookonchain's altcoin tally via FinanceFeeds. Aave: its response thread and LlamaRisk's cap reductions. Liquidations from CoinGlass via FXStreet; prices from CryptoTicker; SAFU size from crypto.news. Our reads on Ethereum mainnet: delegation 0xad99264d5532ae0dd04b2004eebda05f25657e70dacb764f7ac8d4ccd051298b (block 26300753), first sweep 0x53bd38b816c23e74134786c29a8c18d792777998a3b9326047b583100e88e2f3 (block 26300770), delegation removed 0xafbf94c92a8d749988411669fa14d4f8866d9b4420b4ebd299f28e958dac7209 (block 26302920); Binance 14 0x28C6c06298d514Db089934071355E5743bf21d60, sweeper 0x63e842B054Bd624a465454D533C33F573e9c6fAe, operator 0x7c8601d4645b93cea45f71e118a729332e6b5ca0, main receiver 0x5227f603C1eE34CE3C06eFe6477003BDfCCB2f8c, Aave borrower 0x8d53903625b8e839b9df4bd28b0efb1cd6b8639a, shared Bitget address 0x15104a9ce0f08a8f0075a0869ae80e795fe0feb7; Tether AddedBlackList events in blocks 26300954–26301278; Aave V3 Pool Supply/Borrow events in blocks 26300936–26300951 and getUserAccountData and reserve configuration at block 26307577.